Understand what social engineering is, how it is used in digital scams, the risks it creates, and how influence and communication can be applied ethically.
Check it out!
Social engineering is a term widely used in digital security, but the concept goes beyond internet scams.
Simply put, social engineering is the use of knowledge about human behavior to influence decisions. It may appear in digital scams, phishing, fake call centers, urgent messages, and attempts to steal data. But it can also appear ethically in communication, consultative sales, leadership, negotiation, education, and career development.
The difference lies in intent, transparency, and respect for the other person’s decision.
When used maliciously, social engineering tries to deceive, pressure, or manipulate someone to obtain an improper advantage. When used ethically, it helps communicate better, build trust, explain risks, guide choices, and make conversations clearer.
That is why understanding what social engineering is matters not only for protecting yourself from scams, but also for improving communication at work, in business, and in professional life.
What is social engineering?
Social engineering is the practice of influencing a person’s behavior by understanding how they make decisions.
In information security, the term is commonly associated with attempts to deceive users into providing passwords, codes, personal data, account access, or sensitive information.
More broadly, however, social engineering is linked to persuasion, influence, trust, language, context, and human behavior.
The problem is not simply knowing these mechanisms. The problem is using that knowledge to hide intentions, distort information, or induce someone to act against their own interests.
Therefore, there is an important distinction:
- communicating clearly is healthy;
- persuading with arguments is legitimate;
- manipulating by hiding intent is dangerous.
This distinction runs through the entire subject.
In practice, social engineering may appear both in a fake message designed to steal data and in a well-built professional presentation used to explain a decision. Ethics is what separates one from the other.
When there is transparency, freedom of choice, and accurate information, we are talking about legitimate communication and persuasion. When there is deception, hidden pressure, or exploitation of vulnerability, we are talking about manipulation.
Why does social engineering work?
Social engineering works because people do not make decisions based on logic alone.
Decisions are also influenced by trust, haste, fear, curiosity, familiarity, authority, opportunity, and the desire to help.
In many cases, a person does not fall for a scam because they “do not understand technology.” They may be deceived because the situation was constructed to feel urgent, trustworthy, or familiar.
Some factors make social engineering more effective:
- urgency: when it seems the person must act immediately;
- authority: when the message appears to come from someone important;
- familiarity: when the contact seems known;
- fear: when there is a threat of blocking, loss, or harm;
- benefit: when the message promises a reward or opportunity;
- curiosity: when the content creates an urge to click or respond;
- reciprocity: when the person feels they need to give something back;
- trust: when the approach seems to come from a known source.
These factors also exist outside the digital environment. They appear in sales, meetings, negotiations, leadership, presentations, and professional relationships.
The difference is that, in ethical use, they should help make communication clearer. In misuse, they are used to reduce a person’s critical judgment.
So-called mental triggers describe patterns of attention and decision-making. They can be studied to improve a presentation, make a message easier to understand, or structure a proposal better. But they must be used responsibly.
When mental triggers are used to create false urgency, hide risks, or pressure someone into deciding without enough time to evaluate, they stop being communication tools and become manipulation.
When social engineering is misused
Misuse of social engineering occurs when someone tries to obtain an action, information, or advantage through deception.
This may happen in digital scams, fake messages, fake profiles, false call centers, suspicious links, requests for verification codes, exaggerated offers, or attempts to create artificial urgency.
In these cases, the goal is to make the person act without verifying.
The objective may be to steal a password, access an account, obtain personal data, induce a transfer, install a fake app, or collect information for use in later scams.
In digital security, social engineering and phishing often appear together. Phishing is an attempt to deceive a user into clicking a link, opening a fake page, disclosing data, or taking an unsafe action.
An important point: malicious social engineering usually does not begin with technology. It begins with trust.
Before trying to exploit a system, the scammer tries to exploit human behavior. The message may seem urgent. The call may sound official. The profile may look familiar. The link may appear legitimate.
That is why prevention involves simple habits:
- verify the source of the message;
- be skeptical of exaggerated urgency;
- do not share verification codes;
- use official channels;
- confirm requests through another channel;
- review permissions and shared data;
- do not make important decisions under pressure.
For a practical view of data protection and digital scams, also see Digital scams and data protection: how to recognize risks and protect yourself.
Examples of social engineering in everyday life
Examples of social engineering do not need to involve sophisticated attacks.
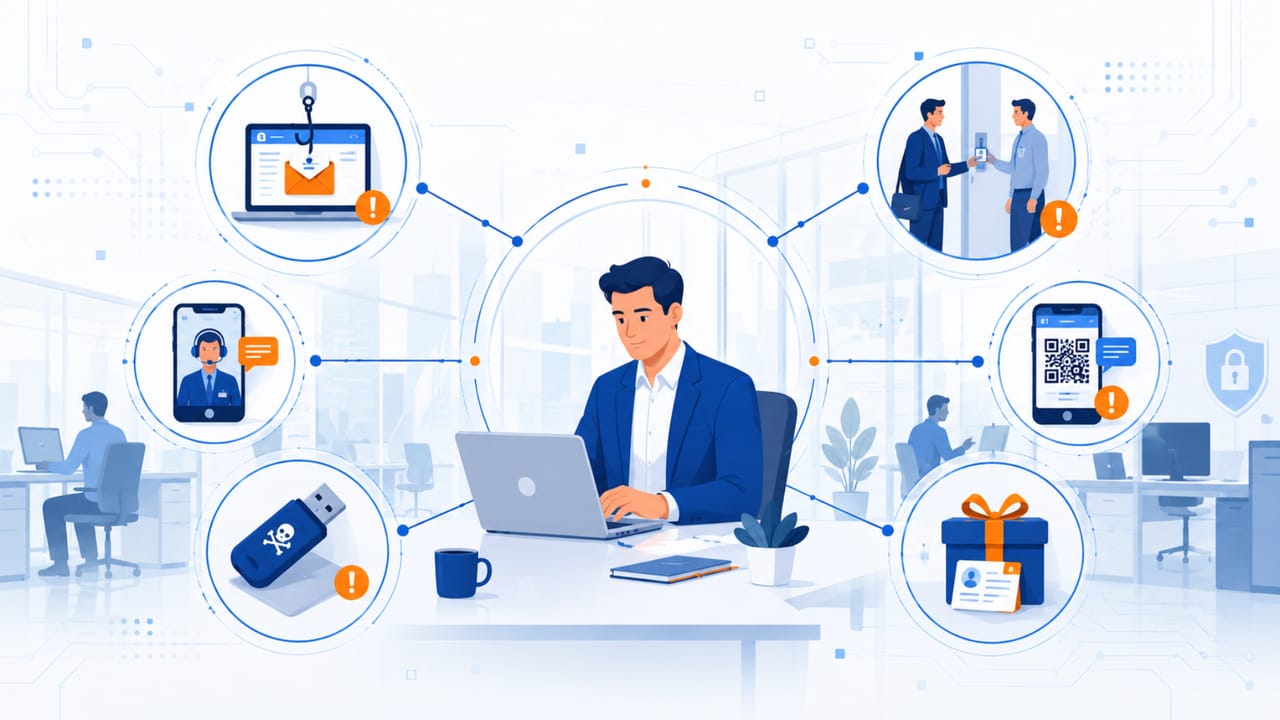
They may appear in ordinary situations, such as a message impersonating a bank, a call pretending to be technical support, an email requesting an urgent account update, or a fake promotion requesting personal data.
They may also appear in professional contexts, when someone tries to accelerate a decision without providing enough information, creates a false sense of urgency, or uses authority to discourage questions.
Examples of social engineering used improperly include:
- fake message claiming an account will be blocked;
- call from a fake customer-service center;
- request for a verification code;
- fake profile asking for financial help;
- email linking to a cloned page;
- form requesting more data than necessary;
- commercial approach that hides important limitations;
- pressure to decide without time for analysis.
The goal here is not to teach how scams work in detail, but to show risk patterns.
When an approach tries to prevent verification, force haste, or capture sensitive data without clear context, it is worth stopping and checking.
Influence and persuasion are not manipulation
One of the most important points about social engineering is separating concepts that are often mixed together.
Influence is the ability to affect a decision, opinion, or behavior. We all influence and are influenced in some way—by people, brands, arguments, experiences, references, and contexts.
Persuasion is the use of arguments, examples, and communication to help someone see value in an idea, decision, or solution.
Manipulation occurs when influence is used dishonestly, hiding information, distorting facts, or exploiting vulnerabilities.
The difference lies mainly in three points:
- intent;
- transparency;
- freedom of choice.
Consultative selling, for example, may use persuasion legitimately when it presents an appropriate solution, explains risks, and respects the client’s decision.
A manipulative approach, on the other hand, creates false urgency, hides limitations, exaggerates benefits, or pressures the person to decide without understanding the context.
In social engineering, this distinction is essential. The same knowledge about human behavior can be used to educate or deceive.
That is why persuasion techniques and persuasive communication must be tied to ethics. They are useful when they make a message clearer, organize arguments, and help someone make a better decision. They become problematic when they hide relevant information or reduce the other person’s autonomy.
How this knowledge can help your career
Understanding human behavior can help significantly in a career, provided it is used ethically.
Professionals who communicate better can explain ideas, defend projects, negotiate deadlines, present risks, build trust, and adapt language to their audience.
This is especially important in technical fields.
An engineer, for example, may have an excellent solution, but still needs to explain why it makes sense, which risks it reduces, which costs it avoids, and how it will be applied in practice.
A career grows when technical knowledge meets clear communication.
Positive applications include:
- presenting an idea more clearly;
- adapting language for non-specialists;
- explaining risks without creating panic;
- defending a technical decision with arguments;
- building trust with clients and teams;
- conducting meetings more objectively;
- negotiating without imposing;
- listening better before proposing a solution;
- turning complexity into understanding.
This is not manipulation. It is good professional communication.
The limit is not distorting reality, not hiding important information, and not inducing someone into a harmful decision.
In an increasingly competitive market, communication is a strategic skill. It is not enough to know a lot; you also need to communicate value, demonstrate responsibility, and build trust.
Rapport, trust, and professional communication
Rapport is a concept associated with building alignment, trust, and openness in a conversation.
In consultative sales, leadership, customer service, negotiation, and career development, rapport can be positive when it comes from genuine listening, respect, and legitimate interest in the other person’s context.
The problem appears when rapport is treated as a performance intended to manipulate.
Building connection does not mean pretending to agree, forcing intimacy, or using personal information to pressure someone. It means creating a conversation in which both parties better understand the problem, expectations, and limits involved.
In engineering, this is especially relevant.
Many technical topics are difficult for people who do not deal with them every day. A professional who builds trust can explain risks, alternatives, and consequences without turning the conversation into a dispute.
Rapport used well creates connection. Rapport used poorly manipulates.
Again, the difference lies in intent.
How companies can use influence ethically
Companies use influence all the time.
A well-written commercial proposal influences. A clear presentation influences. Educational content influences. A trusted brand influences. Good customer service influences.
The question is how that influence is used.
In an ethical approach, the company seeks to understand the client’s real need, present options, explain limitations, demonstrate value, and allow an informed decision.
This appears in consultative sales, customer relationships, training, institutional communication, and leadership.
Healthy practices include:
- active listening;
- clear proposals;
- risk explanation;
- transparency about limitations;
- alignment of expectations;
- customer education;
- language appropriate to the audience;
- commitment to what can actually be delivered.
When a company educates the market, it also influences—but it does so by offering useful information.
This kind of influence is very different from manipulating someone with false urgency, exaggerated promises, or emotional pressure.
A company that sells ethically does not need to hide risk. It shows the problem, presents alternatives, explains limitations, and helps the client decide more safely.
Defensive social engineering: using knowledge to protect people
There is also a defensive use of social engineering.
In this case, the goal is to understand how people may be influenced in order to create better training, policies, procedures, and controls.
Companies can use this knowledge to guide teams, reduce risk, and build a stronger security culture.
This includes explaining how to recognize suspicious messages, validate unusual requests, protect personal data, handle access, and act in high-pressure situations.
The idea is not to distrust everything all the time. It is to create verification criteria.
In connected environments, security depends on technology, but also on behavior.
Cameras, access systems, networks, servers, cloud applications, and connected devices can be well designed and still depend on sound processes and people.
That is why digital security, physical security, and organizational culture are increasingly connected.
In information security, social engineering is a central topic because many incidents begin with a human decision: clicking, trusting, sharing, authorizing, or ignoring a warning sign.
To further explore the connection between physical systems and digital risks, see how to prevent physical-security systems from becoming entry points for cyberattacks.
How to recognize signs of manipulation
Not every attempt at influence is harmful. But some signs deserve attention.
A request may be manipulative when it demands haste without justification, prevents verification, asks for unusual secrecy, uses excessive fear, or promises an unusually large benefit.
Warning signs include:
- request for immediate action;
- emotional pressure;
- threat of blocking or loss;
- exaggerated promise;
- unverified authority;
- request for a password, code, or sensitive data;
- request not to tell anyone;
- link or channel outside the normal pattern;
- lack of transparency about who is making the request.
In professional decisions, the same signals exist.
A negotiation may be problematic when it hides information, imposes an artificial deadline, reduces the possibility of analysis, or uses fear to accelerate a decision.
The best antidote to manipulation is to create time for verification.
In practice, this means asking questions, using official channels, consulting others, requesting written records, and avoiding important decisions under pressure.
Proper use begins with ethics
Social engineering, in its broad sense, shows that human behavior matters.
People make decisions based on information, context, trust, emotion, and perception of risk. Ignoring this makes communication weaker. Exploiting it dishonestly makes communication dangerous.
Proper use of this knowledge begins with ethics.
This means:
- being transparent about intent;
- respecting freedom of choice;
- not hiding relevant risks;
- not promising what cannot be delivered;
- not creating false urgency;
- not exploiting vulnerabilities;
- protecting personal data;
- communicating clearly;
- allowing verification.
When applied correctly, knowledge of human behavior can help people protect themselves, professionals communicate better, and companies build more trustworthy relationships.
The problem is not influencing. The problem is manipulating.
Where A3A Engenharia fits in
A3A Engenharia works in environments where security, technology, processes, infrastructure, and human behavior connect.
In critical systems, electronic security, networks, cloud, data, and infrastructure, reliability depends as much on technology as on procedures and the people involved.
Related technical content
- Digital scams and data protection
- Cloud computing in practice
- Biometrics and Facial Recognition: risks, LGPD, and good practices
- How to prevent physical-security systems from becoming entry points for cyberattacks
- PMBOK for engineers: why project management became a career skill
- What nobody tells you about growing in an engineering career
Related services
Technical references
- ISO/IEC 27001 — Information security.
- ISO/IEC 27002 — Information security controls.
- NIST Cybersecurity Framework.
- CIS Controls — cybersecurity good practices.
- LGPD — Brazilian General Data Protection Law.
- Internal cybersecurity, electronic-security, cloud, networking, and management materials consulted in A3A Engenharia’s static index.
Recommended supplementary materials
FAQ
1. What is social engineering?
Social engineering is the use of knowledge about human behavior to influence decisions. In digital security, it is often associated with scams that try to obtain data, passwords, or access through deception.
2. Is social engineering always bad?
No. Knowledge about human behavior can be used ethically in communication, education, consultative sales, leadership, and security. The problem lies in manipulative or deceptive use.
3. How does social engineering appear in digital scams?
It appears in fake messages, phishing, false call centers, fake profiles, verification-code requests, suspicious links, and attempts to create artificial urgency.
4. What is the difference between persuasion and manipulation?
Persuasion uses clear arguments and respects the other person’s decision. Manipulation hides intentions, distorts information, or exploits vulnerabilities.
5. How can social engineering help a career?
It can help with communication, presenting ideas, negotiation, leadership, defending projects, and building trust, provided it is used ethically and transparently.
6. Can companies use influence ethically?
Yes. Companies can use influence ethically by educating clients, presenting solutions clearly, explaining risks, aligning expectations, and respecting the buyer’s decision.
7. How can people protect themselves from malicious social engineering?
Verify message sources, be skeptical of exaggerated urgency, do not share verification codes, use official channels, and confirm requests through another channel when in doubt.
Conclusion
Social engineering is the use of knowledge about human behavior to influence decisions.
It can be misused in scams, fraud, and attempts at manipulation. But it can also be used positively in communication, career development, consultative sales, leadership, and education.
The difference lies in intent, transparency, and respect for freedom of choice.
Understanding social engineering helps people protect themselves better, communicate more clearly, and recognize when an approach crosses the line between legitimate influence and manipulation.
Does your company consider the human factor in security?
Technology, processes, and people need to work together. A technical assessment can help identify risks in connected systems, access, procedures, and infrastructure.
