The Deep Web is a fundamental and strategic layer of network and web-system architecture. It includes all content, data, and systems not indexed by traditional search engines — beyond the direct reach of conventional search tools such as Google. The Deep Web includes everything from authenticated information and paywalled content to dynamically generated data and internal systems […]
Check it out!
The Deep Web represents a fundamental and strategic layer of network and web-system architecture. It includes all content, data, and systems not indexed by traditional search engines — in other words, resources that fall outside the direct reach of conventional search tools such as Google.
The Deep Web ranges from information accessible only through authentication, paywalled content, and isolated pages without public links to dynamic data generated by applications and institutional portals. Its operation involves specific requirements for protocols, credentials, and advanced security policies.
For engineering, network, telecommunications, and information-security professionals, understanding the Deep Web is essential to protecting privacy and strategic data. Challenges range from logical segmentation of environments to adoption of security best practices, requiring familiarity with standards-based approaches, continuous updates, and effective risk-mitigation policies.
In this article, we discuss the technical fundamentals of the Deep Web, its architecture, access protocols, web segmentation, integration with network infrastructure, security implications, associated threats, and recommendations for protecting systems and data. The objective is to provide a broad view aligned with engineering best practices and regulatory standards for professionals seeking sound references for decision-making, project integration, and risk mitigation.
Read on!
[elementor-template id=”24446″]
What Is the Deep Web? Technical Fundamentals and Applications
The Deep Web is the portion of the internet that is not indexed by search engines such as Google or Bing. It includes internal databases, corporate systems, academic portals, and pages that require authentication or restricted access. In other words, it consists of protected content that is not openly accessible to the general public.
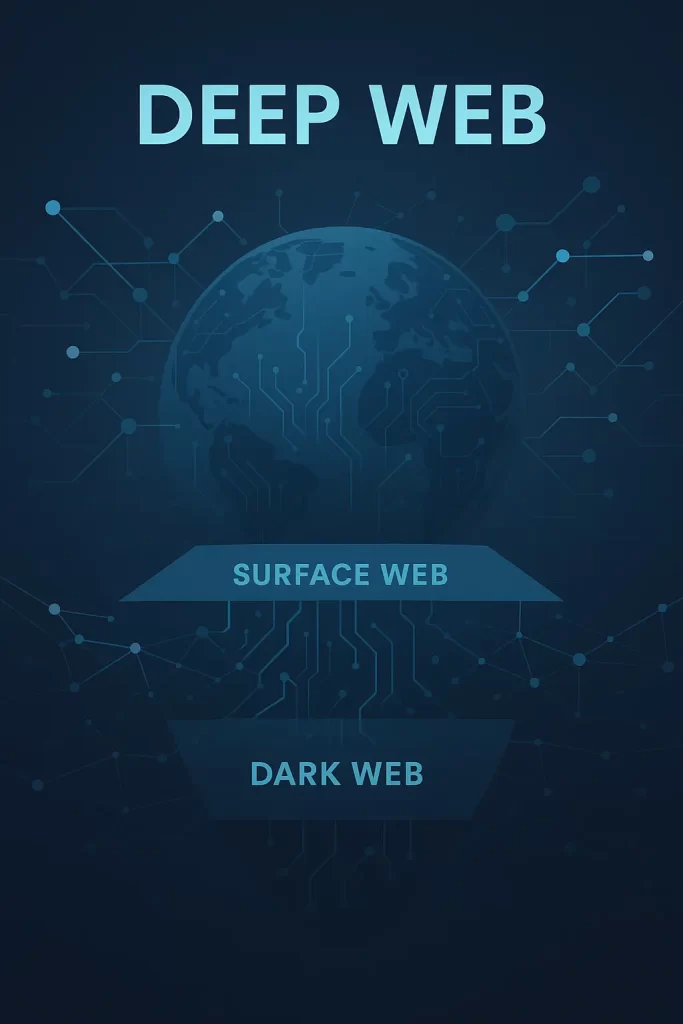
Institutional technical illustration highlighting the Deep Web concept, its layers, corporate examples, and digital-protection elements.
Source: A3A Engenharia de Sistemas.
The Deep Web consists of digital resources, information, and services that are not indexed by conventional search engines.
This includes dynamic application-generated content, protected databases, institutional portals accessible only through authentication, paywalled services, standalone pages without external links, non-HTML content, and multilevel files accessible through credentials.
The growth and diversification of this infrastructure follow the evolution of internet architecture, with areas remaining hidden from public indexers either intentionally or incidentally.
- Dynamic Content: Generated in real time through database queries or application interfaces.
- Confidential Documents and Data: Stored in corporate, academic, or government repositories that require strong authentication.
- Isolated Pages: Resources without public hyperlinks, making automated indexing difficult.
- Paywalled Content: Access conditioned on payment or subscription, deliberately restricting indexing.
Contrary to a common misconception, the Deep Web is not synonymous with criminal or illicit infrastructure. That characterization is more closely associated with the Dark Web, a specific subset of hidden services accessed through anonymizing protocols.
“The Deep Web is not an obscure territory; it is the universe of strategic data and internal systems that support companies, universities, and public institutions. Effective digital security begins with rigorous management of these non-indexed environments, ensuring privacy, compliance, and operational resilience.”
Altair Galvão, Electrical Engineer, Head of A3A Engenharia de Sistemas
How Does the Deep Web Architecture Work and What Are Its Layers?
| Characteristic | Surface Web | Deep Web | Dark Web |
|---|---|---|---|
| Visibility | Indexed by search engines (Google, Bing, etc.) | Not indexed by search engines | Not indexed; access is restricted and anonymized |
| Access | Public and unrestricted through conventional browsers | Restricted: login, authentication, paywall, or specific configurations | Only through dedicated software (e.g., Tor, I2P) |
| Content | Institutional websites, public portals, blogs, news | Internal databases, intranets, corporate platforms | Anonymous marketplaces, forums, whistleblowing channels |
| Anonymity Level | No inherent anonymity | Variable, depending on access control | High, with architecture designed for anonymity and confidentiality |
| Legality | Generally lawful | Lawful except in cases of illicit use | Depends on use and accessed content |
| Examples | www.a3aengenharia.com.br, official government websites | A3A Engenharia intranet, banking systems, academic environments | .onion addresses, anonymous communication services |
Source: A3A Engenharia de Sistemas.
Segmentation Model
- Surface Web: Consists of pages indexed by search engines such as Google. It uses standard HTTP/HTTPS protocols and corresponds to open access.
- Deep Web: A layer of non-indexed resources ranging from internal enterprise systems to academic databases. Access normally depends on authentication, authorization, and specific transport or application mechanisms.
- Dark Web: A more restricted subset accessed through specialized browsers such as Tor, using dedicated addressing and encryption mechanisms designed for strong anonymity.
The segmentation model distinguishes levels of visibility, accessibility, and privacy according to the logical and physical architecture of information systems. The technical difference is functional: while the Surface Web is designed for exposure and indexability, Deep Web resources are intentionally or operationally outside that model.
Access Structures
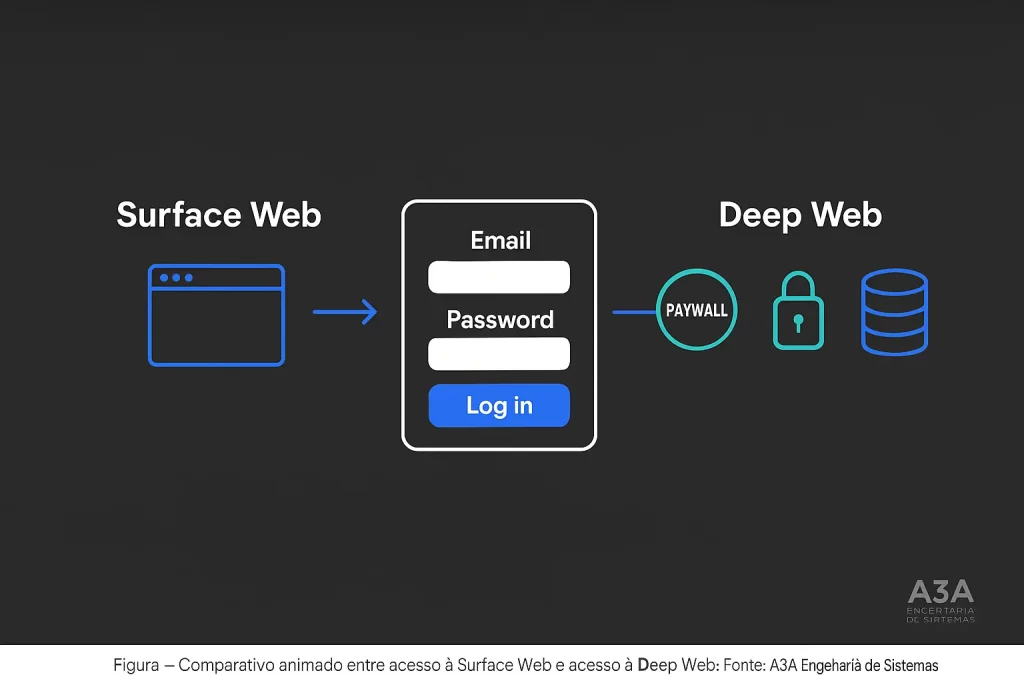
- Authenticated Request: Requires credentials validated by authentication servers.
- Dynamic Content Generation: Data displayed through queries dependent on temporal parameters, filters, and access policies.
- Logical Isolation: Pages, files, and services without explicit links in the open-hyperlink structure.
Deep Web Protocols and Infrastructure: How to Access Securely?
Source: A3A Engenharia de Sistemas.
Deep Web operations involve application-layer protocols, secure transport, segmented routing, and integration with robust authentication and authorization systems. Structures such as VLANs, corporate VPNs, private networks, and controls based on multi-factor authentication (MFA) support much of the traffic and access to these environments.
- Protocols: HTTP/HTTPS, SOCKS5 (specifically in anonymizing environments), TLS for encrypted transport, and specific ports for restricted services.
- Routing: Integration of private and public backbones using advanced logical and physical segmentation mechanisms, structured cabling in accordance with technical standards, and rigorous management of external network interfaces through secure demarcation points.
Typical Topologies
Deep Web network architecture can include external network interfaces, protected entrance infrastructure, and segregated access channels. Physical interconnection points follow structured-cabling recommendations, including pathways, underground cabling, inspection boxes, and mechanical-protection methods intended to reduce interception or sabotage risks.
In enterprise environments, integration between non-indexed internal resources and public networks is performed through segmentation, advanced firewalls, intrusion-prevention systems, persistent access-control lists, and federated authentication, supporting secure interoperability without unnecessary exposure of sensitive data.
Best practices for protecting data in Deep Web environments follow internationally recognized recommendations such as ISO/IEC 27001 (Information Security Management), ISO/IEC 27002 (Security Controls), and ISO/IEC 27005 (Risk Management). These standards guide continuous-update policies, use of advanced cryptography, and segmented access controls that are important in non-indexed environments.
Risks, Threats, and Privacy in the Deep Web: How to Protect Systems and Data
Threats and Risk Vectors
- Data Interception: Traffic in non-indexed environments, when not adequately encrypted, can be subject to sniffing and expose sensitive information.
- Spoofing: Fraudulent operations may impersonate legitimate entities in an attempt to obtain credentials or data without authorization.
- Attacks on Authenticated Systems: Attempts to exploit vulnerabilities in authentication and authorization mechanisms.
- Malware and Remote Exploitation: Environments with weak update controls can become targets for malicious actors seeking progressive compromise.
⚠️ Important:
Unauthorized access to or exposure of data in enterprise Deep Web systems can create serious legal, information-leakage, and operational risks for organizations.
Protection Technologies
- Use end-to-end encryption on applicable communication segments, including TLS and digital certificates issued by trusted certificate authorities.
- Deploy next-generation firewalls with deep-packet inspection and context-based policies.
- Adopt multi-factor authentication and least-privilege access controls.
- Continuously update software, firmware, and applications alongside active vulnerability management.
- Monitor network traffic in real time to identify and mitigate anomalous activity.
Anonymity, Privacy, and Ethical Considerations
The Deep Web, by providing private and restricted-access environments, can strengthen data privacy but also creates ethical and technical challenges. The use of anonymity technologies should remain aligned with applicable law and responsible-use policies, reducing opportunities for abuse or improper exposure.
The processing, storage, and access of sensitive data in non-indexed environments should comply with Brazil’s Lei Geral de Proteção de Dados (LGPD), the European Union’s GDPR, and guidance from Brazil’s ANPD (National Data Protection Authority), supporting digital governance aligned with international best practices.
Compliance and Technical Standards in the Deep Web
- Structured Cabling: Physical infrastructure, including pathways, spaces, dedicated entrances, and system separation, follows technical-standard recommendations to support isolation, integrity, and protection of non-indexed data flows.
- System Security: Access-control systems, physical and logical integrity of components, fault protection, and breach detection are essential in critical environments.
- Updates and Hardening: Adopt continuous-update policies, harden servers and critical segments, maintain current endpoint protection, and block untrusted integrations.
Following these guidelines supports regulatory compliance and increases resilience against sophisticated attack and compromise scenarios.
- Access Control: Implement least privilege, logical segregation of environments, and continuous auditing of permissions assigned to users and third-party systems.
- Monitoring and Backup: Automated backup solutions and periodic copies of data in higher-security environments are essential for critical and high-availability systems.
Deep Web and Electronic Security: Integration and Best Practices
The interface between Deep Web environments and electronic-security systems is increasingly relevant in advanced corporate and building infrastructures. Integrations involving access control, video surveillance, and intrusion-detection systems, when connected through protected non-indexed segments, require reinforced controls for physical and logical integrity.
- Traffic Isolation: Ensure that traffic between security devices and central systems flows through authenticated, encrypted, and monitored channels, reducing interception or manipulation risks.
- Hardening Policy: Apply continuous hardening to connected devices, including firmware and critical-application updates and trusted integration with approved management software.
- Monitoring and Resilience: Detection and incident-response systems integrated with protected network segments support prompt threat identification and data restoration in the event of failure or hostile action.
💡 Technical Tip:
Implement multi-factor authentication policies and regularly review access logs to strengthen the security of non-indexed environments.
Alignment with international physical- and logical-security standards is essential for maintaining the integrity, confidentiality, and availability of interconnected systems in this ecosystem.
Creating and maintaining non-indexed enterprise systems, such as internal databases, intranets, and restricted platforms, requires adherence to infrastructure standards such as TIA/EIA-568 and ABNT NBR 14565, which define practices for structured cabling, system separation, and physical protection of networks.
Frequently Asked Questions
No. Legality depends on use. Unauthorized access to private information or restricted systems may be unlawful.
By using encryption, strong authentication, continuous system updates, access controls, and monitoring.
Data leakage, attacks against authenticated systems, traffic interception, weak access controls, and inadequate segmentation.
The Deep Web includes internet content that is not indexed by traditional search engines, such as databases, internal enterprise systems, academic portals, and restricted website areas that require authentication. It is not inherently ‘secret’; it consists largely of resources not openly accessible to the general public.
Yes. Many mobile banking apps, email services, corporate platforms, and authenticated systems provide access to non-indexed content. Dark Web services, however, use separate technologies and configurations.
The Dark Web is a subset of the Deep Web accessed through specialized protocols and software such as Tor. It is not located in a single physical place; services are distributed across servers in different locations and are not indexed by conventional search engines.
There is no single search engine that indexes the entire Deep Web because much of its content is private, dynamically generated, or access-controlled. Specialized search tools may exist for specific databases or restricted domains.
Conclusion
Understanding and properly managing Deep Web environments requires solid technical knowledge of architecture, access protocols, network infrastructure, logical segregation, and physical and digital protection mechanisms. Non-indexed environments are essential for maintaining privacy, confidentiality, and control of strategic data, but they require rigorous information-security policies, standards alignment, and continuous hardening practices. Integrating critical systems with these environments requires standardized access controls, enhanced monitoring, and readiness for incident response covering both cyber threats and operational risks.
In engineering and security projects, robust segmentation, authentication, and encryption models are decisive for protecting Deep Web environments. Given the pace of technological change, methodologies and tools should be continuously updated, with collaboration across network engineering, IT, and cybersecurity disciplines.
Final Considerations
Exploring the technical landscape of the Deep Web highlights its strategic importance for private, corporate, and institutional environments and reinforces the need for sound engineering and robust security practices. Continuous improvement of controls, aligned with recognized standards and frameworks, can strengthen both resilience and governance.
Thank you for reading this technical article. Follow A3A Engenharia de Sistemas on social media for more specialized content and reference updates on Systems Engineering, Networks, Security, and IT.
Normative References
ISO/IEC 27001 – Information Security Management
ISO/IEC 27002 – Security Controls
ISO/IEC 27005 – Risk Management
TIA/EIA-568 – Structured Cabling
ABNT NBR 14565 – Telecommunications Cabling Infrastructure
“LGPD — Lei Geral de Proteção de Dados (Brazilian General Data Protection Law)”
GDPR – General Data Protection Regulation (EU)
“ABNT NBR ISO/IEC 27001 — Information Security Management”
“ABNT NBR ISO/IEC 27005 — Risk Management”
“CERT.br — Brazilian Center for Security Incident Studies, Response and Treatment”
“NIST Cybersecurity Framework” – National Institute of Standards and Technology
