Understand cybersecurity risks in IP video surveillance, including credentials, privileges, firmware vulnerabilities, insider threats, network exposure, and mitigation.
Check it out!
Cybersecurity measures have become indispensable in video surveillance systems as devices have become integrated with telecommunications networks.
This connectivity has significantly expanded system functionality, enabling greater efficiency and operational flexibility. However, it has also introduced vulnerabilities that can compromise data confidentiality and the integrity of critical operations.
This article addresses the main concepts related to Cybersecurity applied to video surveillance systems, highlighting connectivity-related challenges and the measures needed to mitigate associated risks.
Read on.
[elementor-template id=”24446″]
What is Cybersecurity?
Cybersecurity, also known as cyber security or Digital Security, refers to the set of practices, technologies, and policies designed to protect computer systems, networks, devices, and data against digital threats, unauthorized access, damage, or disruption.
The cybersecurity concept spans multiple layers of protection, from applying encryption to prevent data interception to configuring advanced authentication mechanisms that restrict access to authorized individuals or systems.
Why is Digital Security Important for Video Surveillance Systems?
Improvements in telecommunications infrastructure and local networks accelerated the evolution of video surveillance systems, which naturally began to integrate connectivity-dependent capabilities such as remote access and centralized management.
With the introduction of IP cameras, NVRs, and network-connected DVRs, the need to implement digital security measures became evident.
Exposing these devices to internal networks and the internet — directly or indirectly — creates vulnerabilities that can compromise operational integrity.
Therefore, these systems should be configured and implemented rigorously and in accordance with applicable technical standards.
Common Causes of Data Breaches in Video Systems
Data breaches in video surveillance systems frequently result from weaknesses in security practices, creating vulnerabilities that malicious actors can exploit.
The main vulnerability factors can be categorized as follows:
Weak or Poorly Managed Access Credentials
Weak or poorly managed access credentials are among the main causes of breaches in video surveillance systems.
A 2020 Fortinet study reported that Brazil recorded more than 3.4 billion cyberattack attempts between January and September, out of a total of 20 billion in Latin America.
Many of these attacks use brute-force methods, consisting of repeated attempts to guess credentials by submitting combinations of usernames and passwords until successful.
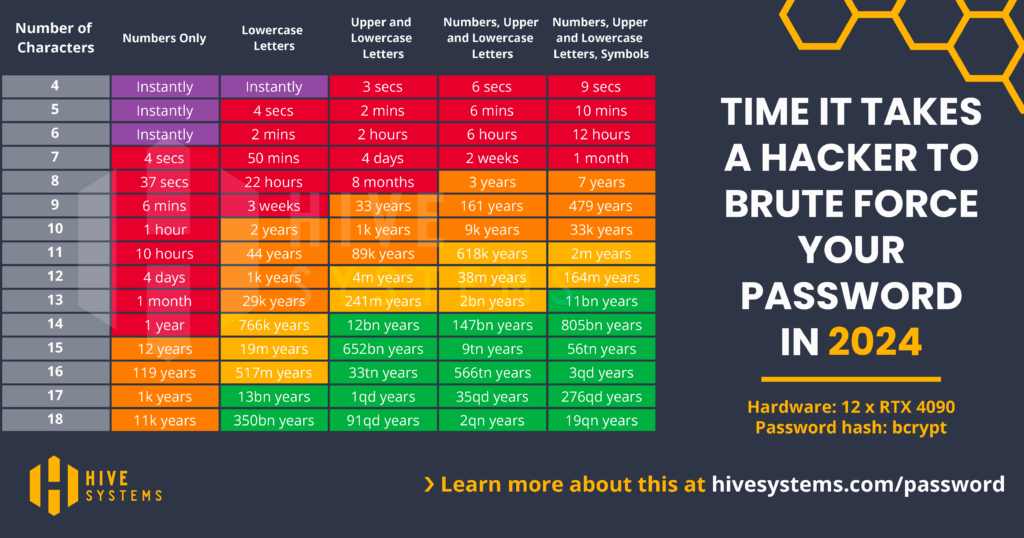
Although widely recognized, weak passwords remain a major entry point for cyberattacks. To mitigate this risk, it is essential to:
- Replace default passwords with strong, complex combinations;
- Use passwords with at least eight characters, including uppercase and lowercase letters, numbers, and symbols;
- Implement policies that avoid predictable patterns such as consecutive repeated characters;
- Establish periodic password-change routines to limit impact in the event of compromise.
Ineffective Privilege Management
Misconfigured privileges are another significant source of vulnerability, enabling unnecessary access to sensitive data and expanding the attack surface.
The principle of least privilege (PoLP — Principle of Least Privilege) should be applied rigorously.
This principle establishes that each user should access only the resources essential to performing their responsibilities.
Neglecting this aspect allows poorly managed credentials to be exploited by malicious actors, whether internal or external.
Excessive privileges compromise system security by enabling improper access that may result in viewing, altering, or deleting critical data.
Users with excessive permissions may also, intentionally or unintentionally, negatively affect operations and facilitate system exploitation by third parties if credentials are compromised.
System security should include regular reviews of permissions assigned to each user, ensuring they remain aligned with specific job functions.
Every change in access levels should be logged and monitored, and temporary permissions should be granted only with documented justification and oversight.
Insider Threats
Insider threats from employees, contractors, suppliers, or partners with legitimate credentials also represent a substantial risk.
These incidents may result from intentional abuse of privileges or negligence in handling sensitive data, causing violations of information integrity and confidentiality.
Rigorous monitoring of user activities, combined with awareness training, is essential to mitigate these risks.
Software Vulnerabilities
Software/firmware flaws are major entry points for malicious actors.
Backdoors, whether intentionally introduced or resulting from development flaws, can allow attackers to access systems covertly.
Malware is also a recurring threat, with programs designed to compromise information, disrupt operations, or exploit systems without administrators’ knowledge.
These vulnerabilities highlight the importance of regular software updates and remediation of known flaws to reduce exploitation risk.
What Can Happen to a Compromised System?
The impacts of a compromised video surveillance system can be extensive, ranging from privacy breaches to legal and financial consequences for organizations and individuals. These scenarios highlight the importance of adopting robust security practices to mitigate risk.
Unauthorized Access and Malicious Surveillance
A compromised system can allow attackers to obtain unauthorized access to live camera feeds.
This may allow them to view and even record monitored surroundings without consent, creating significant vulnerabilities in sensitive environments.
Such control may also be exploited for espionage, facilitating information collection and monitoring of activities for malicious purposes.
Privacy Breach and Personal Impact
Compromised cameras may be directed toward private or sensitive spaces, violating privacy laws and causing harm to monitored individuals.
Exposure of unauthorized images or recordings may create serious legal and ethical consequences, especially in corporate or residential contexts.
Data Theft and Exposure of Sensitive Information
Recordings or images stored locally or on cloud servers may be accessed by malicious actors in the event of a breach.
This exposes confidential information that may be used for blackmail, corporate espionage, or other harmful purposes.
Organizations that fail to protect these data adequately risk significant legal and financial repercussions.
Compromise of Physical Security
By gaining control of the camera system, attackers may manipulate, disable, or create strategic blind spots in surveillance, compromising the physical security of the environment.
This vulnerability is especially critical in high-security locations such as government, financial, or industrial facilities.
Network Vulnerabilities
Compromised devices can serve as entry points for attacks against the broader connected network infrastructure.
Vulnerable cameras may be exploited to move into other devices and systems, expanding the impact of the breach.
Examples of Data Security Vulnerabilities in Video Surveillance
In recent years, a significant number of vulnerabilities have been identified in video surveillance systems, highlighting the importance of rigorous cybersecurity practices.
Many of these flaws originated from improper configurations or the absence of preventive measures, while others were deliberately introduced during device production.
Some documented events illustrate the associated risks:
Botnet Compromise (2014)
DVR devices from multiple manufacturers were targeted by a botnet used for bitcoin mining. The absence of basic security measures such as strong authentication made these devices vulnerable, illustrating the risks of neglecting protection for network-connected equipment.
Mirai Botnet and IP Cameras (2016)
The Mirai botnet compromised thousands of IP cameras from a Chinese manufacturer by exploiting weak, exposed default credentials. Infected devices were used to launch large-scale DDoS attacks, affecting critical infrastructure around the world.
Privilege Escalation in IP Cameras (2021)
A serious vulnerability was discovered in cameras from a Chinese manufacturer, allowing attackers to obtain administrator privileges without valid credentials. This flaw compromised the security of entire networks, especially systems that relied on those cameras for sensitive surveillance.
How Can These Problems Be Prevented?
The solution includes adopting high-quality systems that provide ongoing support, regular updates, and robust security measures.
Devices such as DVRs and NVRs often depend on proprietary firmware with limited updates, making them easier targets for attackers.
Choosing more modern systems, such as servers equipped with VMS software, offers greater flexibility, security, and adaptability to emerging threats.
It is essential to consider Total Cost of Ownership (TCO) in purchasing decisions.
Focusing exclusively on initial camera cost may lead to low-cost, high-vulnerability solutions, increasing attack risk and hidden costs associated with failures or compromise.
Investing in systems that prioritize cybersecurity is therefore a more effective and economical long-term approach.
Final considerations
Vulnerabilities identified in video surveillance systems in recent years reinforce the need to treat cybersecurity as an essential element of any video surveillance project.
Low-cost solutions may appear economically attractive at first, but they often result in systems with significant weaknesses and exposure to risks that compromise data and critical operations.
Experienced security-design companies can assess the specific needs of each environment, identify vulnerabilities, implement high-quality solutions, and ensure that the system follows cybersecurity best practices.
A3A Engenharia is an engineering company specializing in electronic security design, with more than 29 years of market experience.
Conclusion
Thank you for taking the time to explore this essential topic.
If you are considering implementing or improving a video surveillance system, we are available to help you develop the solution best suited to your needs.